Your environment, your models
Runs on your hardware or in your own cloud account, with models inside your boundary or a provider you already use. No connection back to Decision Terrain.
Review deployment optionsDefense & Intelligence
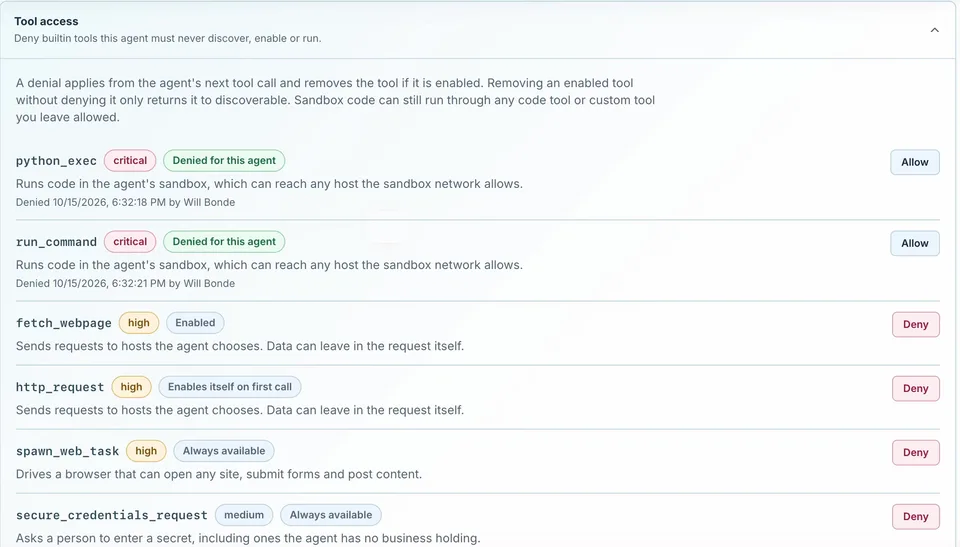
A defense AI platform for persistent agents on your infrastructure, including air-gapped environments, where you decide exactly which tools each agent may use.
Air-gapped deployment
Internal APIs and MCP
Defense and intelligence experience
01 / Your operating environment
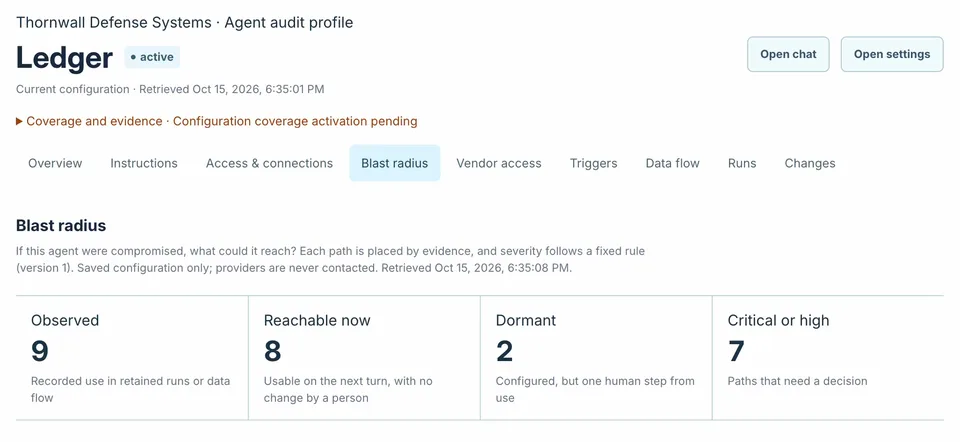
Your infrastructure, model choices, and access rules shape how the work runs. The audit profile shows what an agent could reach if it were compromised, and what still needs a decision.
Watch the blast radius demo. Inspect recorded actions and evidence coverage and the access and approval controls. Place collectors, provider ingestion, and query inside an isolated deployment or leave external routes disabled.
02 / Why security says yes
Most agent projects stall at the security gate, not on capability. Decision Terrain is designed around the three questions an approver asks first: where does the data go, can we stop it, and can we prove what it did.
Runs on your hardware or in your own cloud account, with models inside your boundary or a provider you already use. No connection back to Decision Terrain.
Review deployment optionsDeny tools for one agent, a Team, or everyone. Hold outgoing email for review of the exact message, and require approval for exact API writes. Instructions guide agents; these controls enforce boundaries.
Review security and governanceWhere enabled, place a security hold from the console or from your SIEM, released only by an authorized person. Material actions are recorded before they run and forwarded to your security tools.
Request the security review materials03 / Work your teams can evaluate
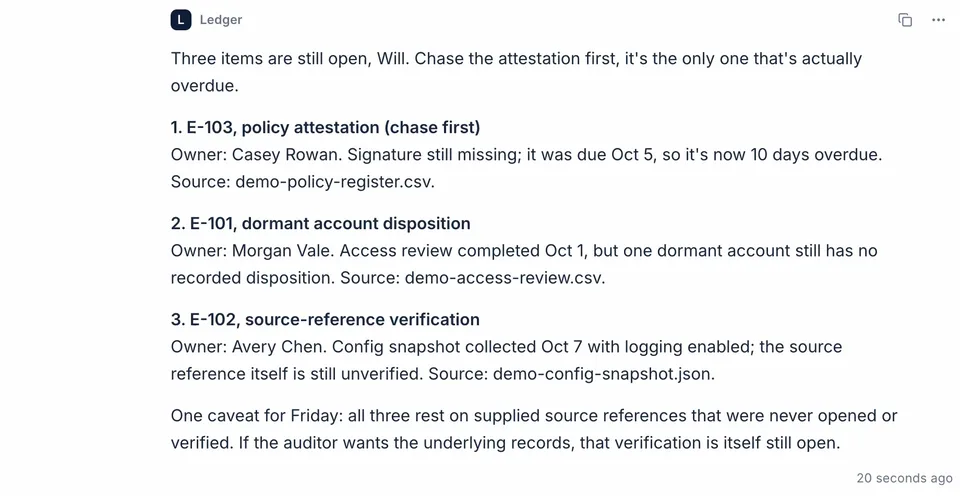
Agents keep instructions, files, and history, so program, technical, and analytical teams get concrete starting points to evaluate.
Illustrative workflows to configure and evaluate, not claims of deployed customer results. Human owners remain responsible for the evidence.
04 / Experience that informs the platform
Defense and intelligence experience shapes how we approach internal systems, operating boundaries, and the people responsible for the work.
Frame the responsibility with its users, sources, authorities, and maintenance needs.
Meet Decision TerrainTest representative assignments, including failure conditions and human checkpoints, before expanding.
Explore evaluation resources05 / Build and implement
Develop capabilities with your own technical team, and add DT expertise where it helps.
Connect APIs and MCP tools, package reusable skills, and use persistent agents from your applications.
Explore developer interfacesAdd DT engineers for deployment, integration, and testing in your environment.
Engineering helpNext steps
Explore the platform around your systems and workflows. Your team can lead implementation, with DT engineering and support available when you need it.